Managed-browser checks
Athena covers supported browser routes, approved tools, warnings and guidance. Request early access to discuss your browsers, tools and data rules.
Use AI. Keep control. Empower your people.
Explore AthenaSet rules for what connected AI tools may receive or send. Give people a reason and a useful next step when sensitive information needs protection.
Use AI. Keep control.
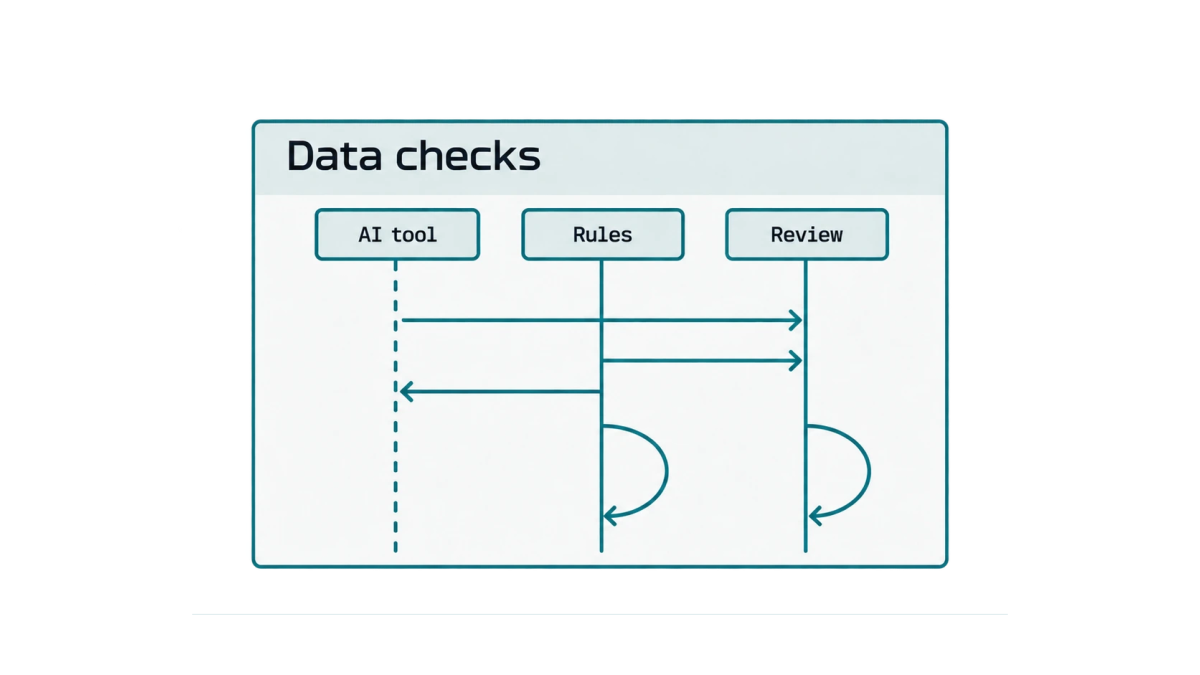
Client records, personal identifiers, credentials and code can enter AI requests. Apply the chosen checks where a supported connection can inspect them.
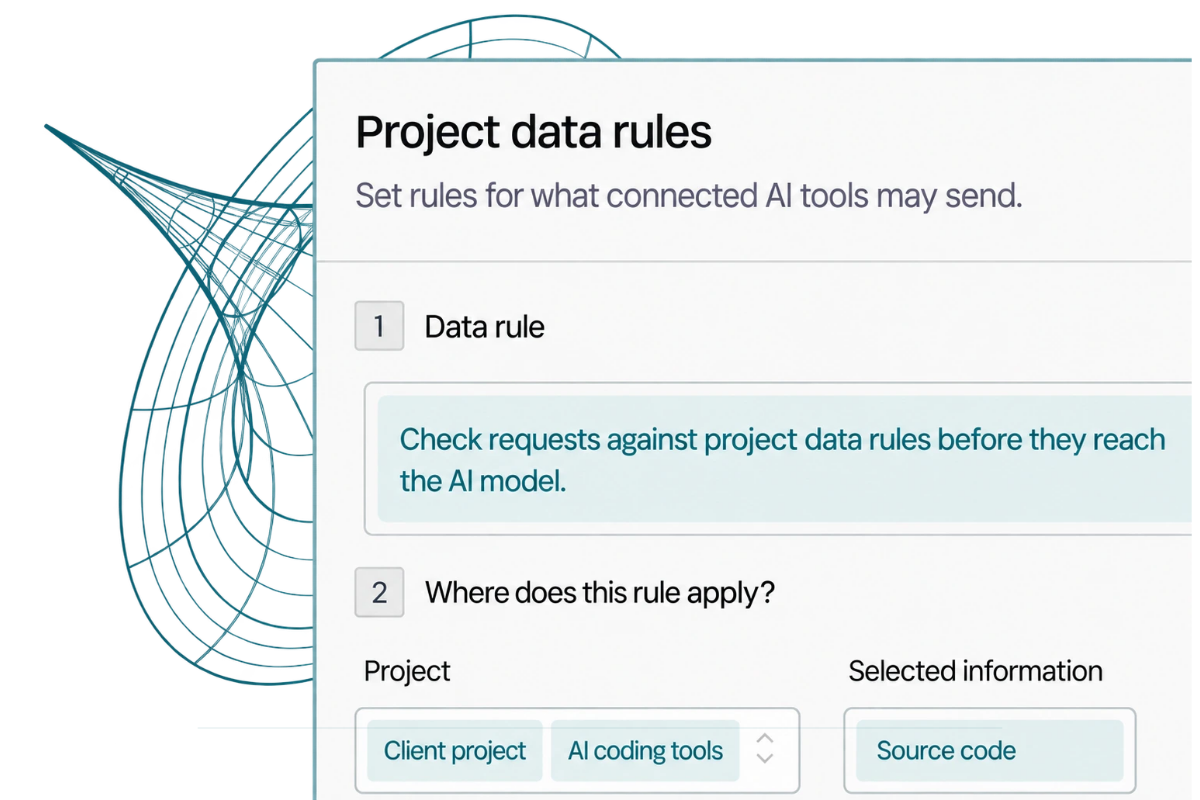
Company and client data
Choose which project material may enter the connected request and which information must stay out.
Requests and destinations
Review the information and destination, including context added by files or tools.
Helpful next steps
Explain the rule and the approved route for continuing the task.
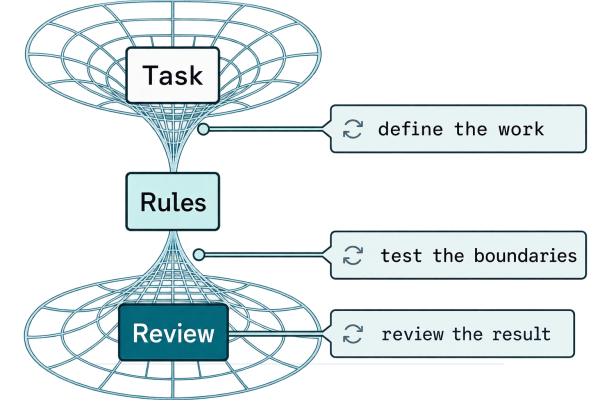
Checks at the supported connection
A supported rule may allow, warn, redact or block. Confirm which behaviour applies to the browser or coding route. A service listing alone does not establish inspection.
Define sensitive data and approved project material. Test the actual tool, version and request route.
Confirm what a warning, block or redaction does before relying on it. Give staff an approved next step.
Review findings and reasons in context. A detector result needs investigation before it is called a confirmed leak.
In practice
Match the information rule to the browser, model request or tool response. Inspection and retention remain separate decisions.
Athena covers supported browser routes, approved tools, warnings and guidance. Request early access to discuss your browsers, tools and data rules.
For Enterprise, map repository context, retrieved material and tool outputs entering the selected model connection. Test permitted and refused requests.
Set rules for the project, data and destination. Review incorrect refusals and missed detections before expanding the workflow.
Name the supported paths and gaps. Decide what to inspect, which records to retain and who can read them.
Data flow and product limitsSee the connection options, set the rules or plan a first test.